• Bhubaneswar India
  • Contact+ 91-9938772605
  • Mon - Sat : 10:00AM - 6:00PM

Category: technology

Check Point Launches Firewall-as-a-Subscription to Put Advanced AI-Era Protection Within Reach of Every Organization

India, Oct 27: Check Point Software Technologies Ltd., a pioneer and global leader in cyber security solutions, today announced the new Firewall-as-a-Subscription program that gives organizations of every size access to Check Point’s most advanced AI security and network threat prevention. Through one predictable subscription, organizations get Check Point Force Firewalls with the AI Network Firewall capabilities introduced in R82.20, AI-powered threat prevention, Live Updates and agentic management, without a large upfront hardware purchase.

Inflation and rising interest rates are increasing borrowing costs and shrinking capital budgets, and for many organizations a single rate rise can wipe out the budget for a planned firewall refresh. Security budgets are under the same pressure. According to the IANS Research and Artico Search 2026 Security Budget Benchmark, the median security budget did not grow this year and 55% of CISOs saw their budgets stay flat or fall. While 64% asked for an increase, only 45% received one. At the same time, AI is increasing what every network has to inspect. When budgets are this tight, firewall refreshes are often among the first projects to slip, leaving organizations on hardware that was never designed for today’s AI-driven traffic and attacks.

Firewall-as-a-Subscription builds on R82.20, which introduced the AI Network Firewall in July 2026 to inspect AI traffic, protect AI applications and help govern AI agents at the network layer. Firewall-as-a-Subscription is the next step in Check Point’s mission to secure AI transformation, making that protection available to organizations of every size and budget.

“Organizations of all sizes face the same AI-driven threats, but for many, capital budget cycles often force them to delay firewall refreshes or buy more capacity than they need,” said Pete Finalle, Research Manager, Security and Trust at IDC. “Consumption models that turn on-premises security hardware into a predictable operating expense, and let organizations scale protection as their needs grow, can help close that gap. We expect demand for this kind of flexibility to rise as AI adoption increases the traffic and risk networks must handle.”

What Firewall-as-a-Subscription includes:

  • AI Network Firewall: the R82.20 capabilities that inspect AI traffic, protect AI applications and help govern AI agents at the network layer

  • Check Point Force Firewalls: sized and priced on the threat prevention throughput the organization needs

  • AI-powered threat prevention: including SandBlast, with a 99.9% block rate against zero-day attacks

  • Live Updates: security updates applied on the fly, with no reboots or downtime

  • Smart-1 Agentic Management package: cloud-based security management with no additional on-premises infrastructure

  • Premium support: 24×7, with direct or collaborative options

  • Professional services: Check Point Global Services Flex Credits that cover policy migration from another vendor’s firewall, or other Check Point services

“Every organization is adopting AI, and every organization deserves the same level of protection, whatever its size or budget,” said Avi Rembaum, President Global Technical Sales at Check Point Software Technologies. “With Firewall-as-a-Subscription, we are making our most advanced AI security, threat prevention and agentic management available through one simple subscription, so organizations can secure their AI transformation today.”

Organizations pay one predictable monthly or annual subscription instead of buying hardware upfront. They can upgrade throughput at any time during the three-year term and move to new hardware after 36 months, so protection keeps pace with AI adoption and business growth.
Cohesity Data Cloud Becomes the First Cloud Recovery Method Validated for Interoperability with IBM Terraform Self-Managed

India, Oct 27: Cohesity, the leader in AI and data security, today announced that HashiCorp, an IBM Company, has validated the interoperability of Cohesity Data Cloud’s cloud rebuild capabilities with Terraform Self-Managed. Organizations can now quickly recover cloud applications – infrastructure, configuration, and, most importantly, data – after a destructive cyberattack. The Terraform product can recreate the compromised declared configuration; Cohesity Data Cloud then restores the latest usable application data from backup. 

This is the first cloud recovery method IBM has validated for interoperability with Terraform Self-Managed, self-hosted platform for defining and managing cloud infrastructure as code. Cloud rebuild is part of Cohesity Data Cloud Enterprise Edition.

Rebuild the declared configuration and restore the data

AI is increasing the frequency and severity of cyberattacks, and recovery plans haven’t kept pace. Cohesity’s 2026 Global Cyber Resilience Report, a Vanson Bourne survey of 3,200 security and IT decision-makers, found that 83% of surveyed organizations said their recovery plans would need moderate or significant changes to handle attacks that use AI to find and exploit software weaknesses. Only 3% say their plans are ready today. Cloud recovery also lags. When an attack compromises a cloud application, IT teams often rebuild it by hand or rely on tools that piece the environment back together using bespoke methods. 

Cohesity cloud rebuild takes a different approach. It uses an organization’s infrastructure-as-code files, which define its cloud networks, servers, and access permissions, as the blueprint for recovery. Terraform uses the organization’s reviewed and approved code to recreate the declared configuration, and Cohesity Data Cloud restores the latest usable backed-up application data. Together, they return the application to a trusted state rather than to a copy that may already contain an attacker’s changes. 

Some recovery tools restore a copy of production as it looked just before an attack, which can include errors or changes made by the attacker. Cloud rebuild instead restores the environment described by the organization’s own reviewed and approved code, returning applications to their declared configuration and restoring protected data from the selected backup.

Cohesity cloud rebuild can read applications through Terraform’s official interface and runs customers’ code unchanged, maintaining record accuracy. Terraform code recreates the declared configuration, while Cohesity restores application data from backup. What’s more, administrators can integrate cloud rebuild into existing incident response and recovery workflows.

“Attackers using AI move faster than any team can rebuild by hand. Organizations have already codified exactly what their cloud environments should look like in Terraform. Cohesity uses that code to recreate the declared configuration, then restores the latest usable application data from backup. Teams need both to bring the application back. If you build as code, you can now recover as code,” said Vasu Murthy, chief product officer, Cohesity. 

“Our customers have asked how they can recover from an attack leveraging Terraform and it’s state, and not just build a new environment,” said Tyler Lynch, Outbound CTO, Automation, IBM Software. “We worked with Cohesity to validate how our technologies work together when they use Terraform state to recover cloud applications, the infrastructure they run on, and the data as part of the recovery process.”

Cohesity Data Cloud + Terraform Self-Managed: How it works

Here’s what happens from protection through recovery: 

  • Map the application. Cloud rebuild reads the organization’s Terraform code and creates a detailed map of each cloud resource that needs protection and the order in which resources should be restored.

  • Save trusted versions. Cloud rebuild backs up both the Terraform code and the application data over time, so teams can choose a recovery point that pairs the intended configuration with backed-up application data.

  • Rebuild step by step. Cloud rebuild recreates the declared infrastructure and configuration from Terraform code, then restores application data from the latest usable backup for that recovery point. For databases such as Amazon RDS, a guided multistep process walks administrators through reconnecting the restored database to the rest of the application.

  • Show the timing gap. Because infrastructure and data can be backed up on separate schedules, Cloud rebuild pairs the closest data backup with the chosen code version and clearly shows how far apart in time the two are. Teams can see which data backup the recovered application will use.

A Third of Young Adults Turn to Artificial Intelligence for Substance-Use Information

Oct 26: More than 32% of participants in a Rutgers study reported using ChatGPT and similar chatbots for substance-use information.

Rutgers Health researchers used survey data from nearly 1,000 participants to examine the frequency and characteristics of people turning to generative artificial intelligence (AI), a subfield of AI that creates synthetic content in response to user prompts, for substance-related information and their perceptions around the results produced by AI.

Recent survey data shows that 66% of young adults use AI to search for information and to get medical advice, among other purposes. Rutgers investigators aimed to better understand how young adults use AI specifically to get information about substances and substance use.

The study, published in the Journal of Medical Internet Research Formative Research, found that 1 in 3 people ages 18 to 29 use AI for substance use–related information, primarily seeking information on risks and consequences. Researchers said their findings were concerning, considering AI chatbots can reproduce misinformation.

“Using these tools can lead to misinformed or otherwise risky substance-use behavior among young people, who are the age group most affected by adverse effects of substance use,” said Mireia Triguero Roura, a postdoctoral researcher with the Center for Pharmacoepidemiology and Treatment Science at Rutgers Institute for Health, Health Care Policy and Aging Research and lead author of the study.

About half of the respondents who use AI for substance use-related information reported doing so on at least a monthly basis. The study, coauthored by Pia M. Mauro, an associate professor at the Center for Pharmacoepidemiology and Treatment Science and Rutgers School of Public Health, also found that Black and male participants were more likely to use AI for substance use–related purposes.

“The observed disparities in who chooses to use AI for drug-related inquiries could reflect differences in healthcare access, stigma, trust, and health information-seeking behaviors,” said Triguero Roura.

Researchers also analyzed respondents’ feelings toward AI, reporting that young adults in the study perceived high levels of trust, reliability and helpfulness of AI tools.

As AI continues to shape the substance-use information available to young adults, Triguero Roura and Mauro suggest additional research should explore how young adults interpret and understand the outputs of AI when it relates to drugs and alcohol as well as the implications of this new source of information on public health.

Where Are They Now: Team Atlanta Takes AI Cybersecurity Beyond the Competition

Oct 26: Team Atlanta spent two years exploring how artificial intelligence could help identify and fix software security problems as part of the Defense Advanced Research Projects Agency AI Cyber Challenge.

After a grueling, world-class competition, the team won the $4 million first-place prize in August 2025. 

The team has since disbanded. Some members have moved into the corporate world, while others continue in academia. Despite these varied paths, Team Atlanta’s search for breakthrough AI cybersecurity solutions continues.

From AIxCC to Microsoft

Team Atlanta lead Taesoo Kim, principal security researcher Dongkwan Kim, and three other former team members joined Microsoft Security after the competition, where they continue to work on AI and cybersecurity in the Frontier Offensive Research & Generative Exploitation (FORGE) Lab.

The move has given the researchers an opportunity to apply concepts from AIxCC to real-world software. It has also exposed them to challenges that are difficult to replicate in a competition or research lab.

Dongkwan Kim said that team members continue to share what they learned through research papers, reports, software, and benchmarks. At Microsoft, these lessons are tested against real customer code.

This work led to MDASH, Microsoft’s multi-agent, multi-model system for vulnerability discovery and remediation. The system uses more than 100 AI agents to search for vulnerabilities, validate potential findings, and help develop fixes.

Rather than asking a single AI model if a piece of code contains a vulnerability, MDASH can examine a problem using multiple agents. The system can also try to create an exploit to determine whether a potential vulnerability is real and reachable.

For Dongkwan Kim and the other former Team Atlanta members at Microsoft, moving from AIxCC to MDASH showed how research can look different when applied to real software.

“AIxCC was not an endpoint for Team Atlanta,” he said. “We continue sharing what we learned through technical reports, papers, open artifacts, and benchmarks for vulnerability discovery and patching.”

Working with customer code introduced new challenges for the Microsoft team. The researchers had to consider security boundaries, existing development processes, how findings would be reviewed, and how vulnerabilities would be prioritized for action.

These challenges created a new feedback loop between research and product development. The team took ideas from AIxCC, test them on real software, learn where they worked and where they fell short, and use those lessons to improve the system.

The experience also showed that AI does not replace the need for cybersecurity experts. Human researchers are still needed to provide context, decide how to break down difficult problems, validate findings, understand attack paths, and determine the potential impact of a vulnerability.

Taesoo Kim, a professor in the School of Cybersecurity and Privacy and vice president of security research at Microsoft, said the competition continues to influence the Microsoft team’s work.

“Every single activity that we’ve done at Microsoft was influenced by AIxCC,” he said in a 2026 interview with Microsoft.

The work has continued to grow. In 2026, Microsoft introduced MAI-Cyber-1-Flash, an AI model built specifically for cybersecurity and designed to work with MDASH.

The model is designed to handle many of MDASH’s tasks while allowing larger AI models to focus on harder problems. Microsoft reported that replacing 80% of the models used by MDASH with MAI-Cyber-1-Flash increased its performance on the CyberGym benchmark from 88.4% to 95.95%.

The benchmark includes more than 1,500 examples from 188 software projects. Microsoft also reported that the new setup can achieve similar performance at half the cost of the previous MDASH configuration.

“AIxCC has sparked cybersecurity innovation across the globe, from frontier AI companies to small academic labs,” said Taesoo Kim. “It is an incredibly exciting time to be working in AI-driven security engineering and research, as we see AI fundamentally reshape how we find and fix vulnerabilities at scale.”

Continuing the Research at Georgia Tech

The AIxCC experience also continues to shape cybersecurity research at Georgia Tech.

Jiho Kim, a Georgia Tech Ph.D. student who was part of Team Atlanta’s research efforts, said one of the biggest lessons he’s brought back to campus was learning how AI and traditional security tools can work together.

One of these tools is fuzzing. Fuzzing tests software with large numbers of inputs to detect unexpected behavior or security problems. Large language models (LLMs), meanwhile, can reason about code and help guide the search.

During the AIxCC competition, the Team Atlanta combined these ideas in CtxFuzz, a system that uses an LLM to help guide fuzzing toward parts of software that may contain vulnerabilities.

The research was submitted to the ACM/IEEE International Conference on Automated Software Engineering, where it received the ACM Distinguished Paper Award.

“Since AIxCC, we’ve continued building on some of the core findings from our two-year journey with Team Atlanta,” Jiho Kim said.

“One of the biggest lessons for us was understanding how LLMs and traditional fuzzing can work together in a mutually beneficial way, using each to overcome the limitations of the other and ultimately find more and deeper vulnerabilities.”

The researchers also wanted to make the lessons from AIxCC useful to other cybersecurity researchers.

They created an Open-Source Cyber Reasoning System Framework and CRSBench, which provides researchers and security professionals with ways to use, test, and build on technology developed through AIxCC.

“We’ve also been focused on making the results of AIxCC useful to the broader security community,” Kim said. “We created OSS-CRS and CRSBench so that researchers and practitioners can more easily use, reproduce, and build upon the capabilities and lessons from our AIxCC work.”

The team’s research has also moved beyond identifying vulnerabilities. Researchers are studying how well AI models can understand and reason about computer code.

Jiho Kim and his lab mates in the Systems Software & Security Lab developed COIN, a benchmark designed to test how well LLMs can reason about code. The work has been accepted to the 2026 Conference on Empirical Methods in Natural Language Processing.

The Georgia Tech researchers are also developing additional benchmarks to study the various types of reasoning required for cybersecurity. They are using what they learn to create new datasets and methods for training AI models focused on cybersecurity.

“We’re using what we learn from these benchmarks to train cybersecurity-focused models through new datasets and training methodologies,” Jiho Kim said.

How Cybersecurity Startups Are Addressing Emerging Business Risks

How Cybersecurity Startups Are Addressing Emerging Business Risks

Cybersecurity has become a critical business priority as companies increasingly depend on digital platforms, cloud services and online transactions. From protecting customer information to keeping daily operations running, businesses must manage growing threats such as ransomware, data breaches, identity theft and AI-driven attacks. For small businesses and growing enterprises, a single cyber incident can lead to financial losses, operational disruption and damage to customer trust. This growing need for reliable protection is creating new opportunities for cybersecurity startups, which are developing smarter, more accessible solutions to help businesses identify threats early and strengthen their digital security.

Why Cybersecurity Matters for Businesses

As companies adopt more digital tools, their exposure to cyber risks also increases. Customer databases, financial records, employee accounts and business applications can become targets if security controls are weak.

For businesses, the consequences extend beyond technology. A cyberattack can interrupt services, delay payments, increase recovery costs and weaken customer confidence. Investing in cybersecurity is therefore becoming an essential part of business continuity and long-term risk management.

AI Is Changing Cybersecurity

Artificial intelligence is creating new opportunities for businesses, but it is also changing how cyberattacks are carried out. Attackers can use automated tools to create convincing phishing messages, identify system weaknesses and increase the speed of their operations.

Cybersecurity startups are responding with AI-powered solutions that analyse system activity, detect unusual behaviour and help security teams investigate potential threats. Some are also developing tools to protect AI applications against data leakage, manipulation and unauthorised access.

Although automation can improve detection and response times, businesses still need human oversight, regular security testing and clear procedures for handling incidents.

Cloud Security and Data Protection

Cloud computing enables businesses to store information, run applications and expand operations without making large investments in physical infrastructure. However, misconfigured systems, exposed application programming interfaces (APIs) and poorly managed software access can create security gaps.

Cybersecurity startups are developing tools that monitor cloud environments, identify vulnerabilities and help companies secure applications throughout their development. Addressing weaknesses early can reduce the risk of costly disruptions and support safer digital expansion.

Stronger Identity and Access Management

Weak passwords, shared accounts and excessive user permissions can give attackers access to sensitive business systems. These risks can become harder to manage as companies hire more employees and work with external service providers.

New security solutions are helping businesses strengthen authentication, monitor suspicious account activity and restrict access to essential information. Zero-trust security, which requires users and devices to be verified before access is granted, is also gaining importance.

For growing businesses, effective identity management can help prevent unauthorised access while ensuring employees have the permissions they need to perform their work.

Managing Ransomware and Supply Chain Risks

Cybersecurity risks do not always originate within a company. External software providers, payment platforms and other business partners can introduce vulnerabilities into connected systems.

Startups are developing tools to assess third-party risks, monitor software weaknesses and identify potential entry points for attackers. These capabilities can help businesses understand where their digital operations may be exposed.

Ransomware remains another serious concern because attackers may steal sensitive information, encrypt systems and threaten to release confidential data. Regular backups, continuous monitoring and a tested incident response plan can help companies reduce disruption and recover more effectively.

Affordable Cybersecurity for Small Businesses

Many small businesses lack dedicated security teams and have limited budgets for advanced technology. This creates demand for subscription-based cybersecurity services that provide monitoring, vulnerability assessments and security alerts without requiring a large upfront investment.

For cybersecurity startups, this represents an opportunity to serve businesses that need stronger protection but cannot manage complex enterprise systems. Easy-to-use tools, transparent pricing and access to specialist support can make cybersecurity more practical for smaller organisations.

Businesses should still evaluate the effectiveness of a solution, the provider’s data-handling practices and the level of support available before making a decision.

The Business Opportunity for Cybersecurity Startups

As digital adoption expands, businesses need security solutions that can keep pace with changing threats without slowing down innovation. This creates opportunities for cybersecurity startups to develop specialised products for cloud infrastructure, AI applications, identity protection and regulatory compliance.

Companies that deliver reliable protection, integrate smoothly with existing systems and demonstrate clear business value can address an important market need. However, long-term success will depend on building customer trust, responding to evolving threats and maintaining strong technical standards.

Conclusion

Cybersecurity startups are playing an increasingly important role in helping businesses manage digital risks and protect their operations. By making security tools more automated, accessible and adaptable, they are helping organisations strengthen protection without relying entirely on large internal technology teams.

For businesses, cybersecurity is no longer just an IT expense; it is an investment in continuity, customer confidence and sustainable growth. Companies that combine effective security technology with employee awareness, regular system updates and clear recovery plans will be better prepared to manage emerging threats. As digital business expands, the demand for practical cybersecurity solutions is likely to remain an important opportunity for innovation and growth.

Submer to Address the Infrastructure Challenges Behind Sovereign AI at DCD Connect | MENA 2026

Dubai, United Arab Emirates, Oct 24:  Submer, a full-stack AI and HPC data centre infrastructure provider, will join industry leaders at DCD Connect | MENA 2026, taking place October 26–27 at Grand Hyatt Dubai, to discuss the infrastructure strategies needed to advance sovereign AI across the region.

As governments and organisations across the Middle East accelerate their sovereign AI and cloud strategies, the challenge extends beyond keeping data within national borders. They must also build the high-performance computing infrastructure needed to support increasingly complex AI workloads while meeting regulatory requirements, scaling efficiently and maintaining commercial viability.

Submer will contribute to this discussion through its participation in the panel debate “Building Sovereign AI: Enabling Innovation Through Scalable Compute,” on October 26, from 2:30 p.m. to 3:15 p.m. The session will explore the infrastructure requirements of sovereign cloud environments, the trade-offs between fully localised and hybrid infrastructure models, and how the region can develop a sovereign-ready compute backbone without compromising flexibility, performance or return on investment.

Bahaa Al Janabi, Technical and Solution Lead for Middle East, Turkey and Africa at Submer, will join fellow industry experts to examine how infrastructure decisions can shape the region’s ability to turn its AI ambitions into scalable, commercially viable deployments.

Submer to Address the Infrastructure Challenges Behind Sovereign AI at DCD Connect | MENA 2026


“Sovereign AI is not simply about where data resides. It is about having the infrastructure to run advanced AI workloads at scale while meeting national requirements and making the economics work. The choices organisations make today will shape their ability to innovate, scale and compete. We look forward to discussing how the right infrastructure strategies can help turn the region’s sovereign AI ambitions into reality,” said Bahaa Al Janabi.

Submer representatives will also be available throughout the event to meet with customers, partners and industry stakeholders and discuss the evolving AI infrastructure landscape across the Middle East, Africa and Turkey.

India Ranks 11 Among the 18 Most Affected Countries in PHP2Shell Attacks: Check Point Research

Oct 23: India has recorded a PHP2Shell impact rate of 14%, above the global average of 10%, according to Check Point Research. This places India among the 11th-highest impact-rate positions in the country rankings, alongside Norway and Ukraine at 13% and behind the European countries with higher reported rates.

What PHP2Shell is and why it matters

The two vulnerabilities sit in the PHP engine itself. That puts a vast range of technology in scope: websites and online stores running WordPress, Drupal, Joomla or Magento, shared hosting platforms, cPanel and Plesk control panels, and many commercial applications. An attacker can exploit the flaws to run their own code on a vulnerable server remotely, without logging in. That can lead to data theft, attacks on other connected systems, or service outages.

Two things have made the situation more urgent. Details of the vulnerabilities leaked before the planned disclosure, which gave attackers a head start and shortened the time defenders had to prepare. And screenshots of a PHP2Shell attack tool targeting the flaws have begun to circulate, a sign that exploitation is moving from theory to practice.

Europe has been hit more than twice as hard as other regions

14% of organisations in Europe have been impacted since disclosure, more than double the 6% recorded in North America, Latin America and APAC. Africa has the lowest regional rate at 4%.

16 of the 18 most affected countries are in Europe

Hungary has the highest impact rate in the world, with 38% of organisations affected since disclosure. Denmark follows at 32% and Austria at 28%, with Sweden and Romania at 22% each. Portugal, Thailand and Serbia each recorded 17%, followed by Germany at 16% and the Netherlands at 15%. India recorded 14%, Norway and Ukraine 13%, and Czechia, Poland, Spain, Switzerland and the United Kingdom 12% each. Thailand and India are the only countries outside Europe in that group. Just behind them, Turkey recorded 11%, and Ireland, Brazil and Italy 10%.

Lotem Finkelstein, Vice President of Research, Check Point Software Technologies

“The concern surrounding PHP2Shell stems from the combination of the vulnerabilities’ severity and the widespread use of PHP, which underpins websites, e-commerce platforms, and many enterprise services. The two critical vulnerabilities could allow attackers to execute code remotely, and the leak of their details ahead of the planned disclosure is narrowing the window for security teams to prepare. Because these vulnerabilities reside in the PHP engine itself, updating a content management system or its plugins alone is not enough.

Addressing the threat starts with three things: understanding your exposure, ensuring your infrastructure can be patched quickly, and preparing compensating controls for cases where immediate patching is not possible. You cannot protect a system you do not know exists. Organizations therefore need to inventory all their PHP instances, including those in containers and third-party products, prioritize internet-facing servers, and pay particular attention to versions that are no longer supported. Identifying a vulnerability is important, but being able to fix it quickly is equally essential.

AI is accelerating vulnerability discovery and exploitation, leaving security teams less time to respond. Alongside preparing to deploy official updates as soon as they become available, organizations should activate layers of protection and monitor for suspicious activity, such as web server processes executing system commands, new files appearing on websites, or outbound connections to unknown destinations. We continue to monitor the situation and update our analysis as new information becomes available.”

Telecoms and education are the most exposed industries

Telecommunications recorded the highest impact rate at 20%, twice the global rate, followed by education at 18%. Media and entertainment and associations and non-profits each recorded 16%. Agriculture and transportation and logistics each recorded 14%, followed by software and healthcare and medical at 13%. Information technology recorded 12% and business services 11%.

Real estate, rentals and leasing; automotive; aerospace and defence; industrial manufacturing; and government each recorded 9%. Hardware and semiconductors, consumer goods and services, financial services, and construction and engineering each recorded 8%. Wholesale and distribution recorded 7%, while energy and utilities and hospitality, travel and recreation each recorded 6%. Biotech and pharmaceuticals recorded the lowest rate of the 23 industries tracked, at 5%.

Latest Medical Aesthetic Technologies and Regenerative Treatments to Be Showcased at ASLS Korea 2026 Autumn

Latest Medical Aesthetic Technologies and Regenerative Treatments to Be Showcased at ASLS Korea 2026 Autumn

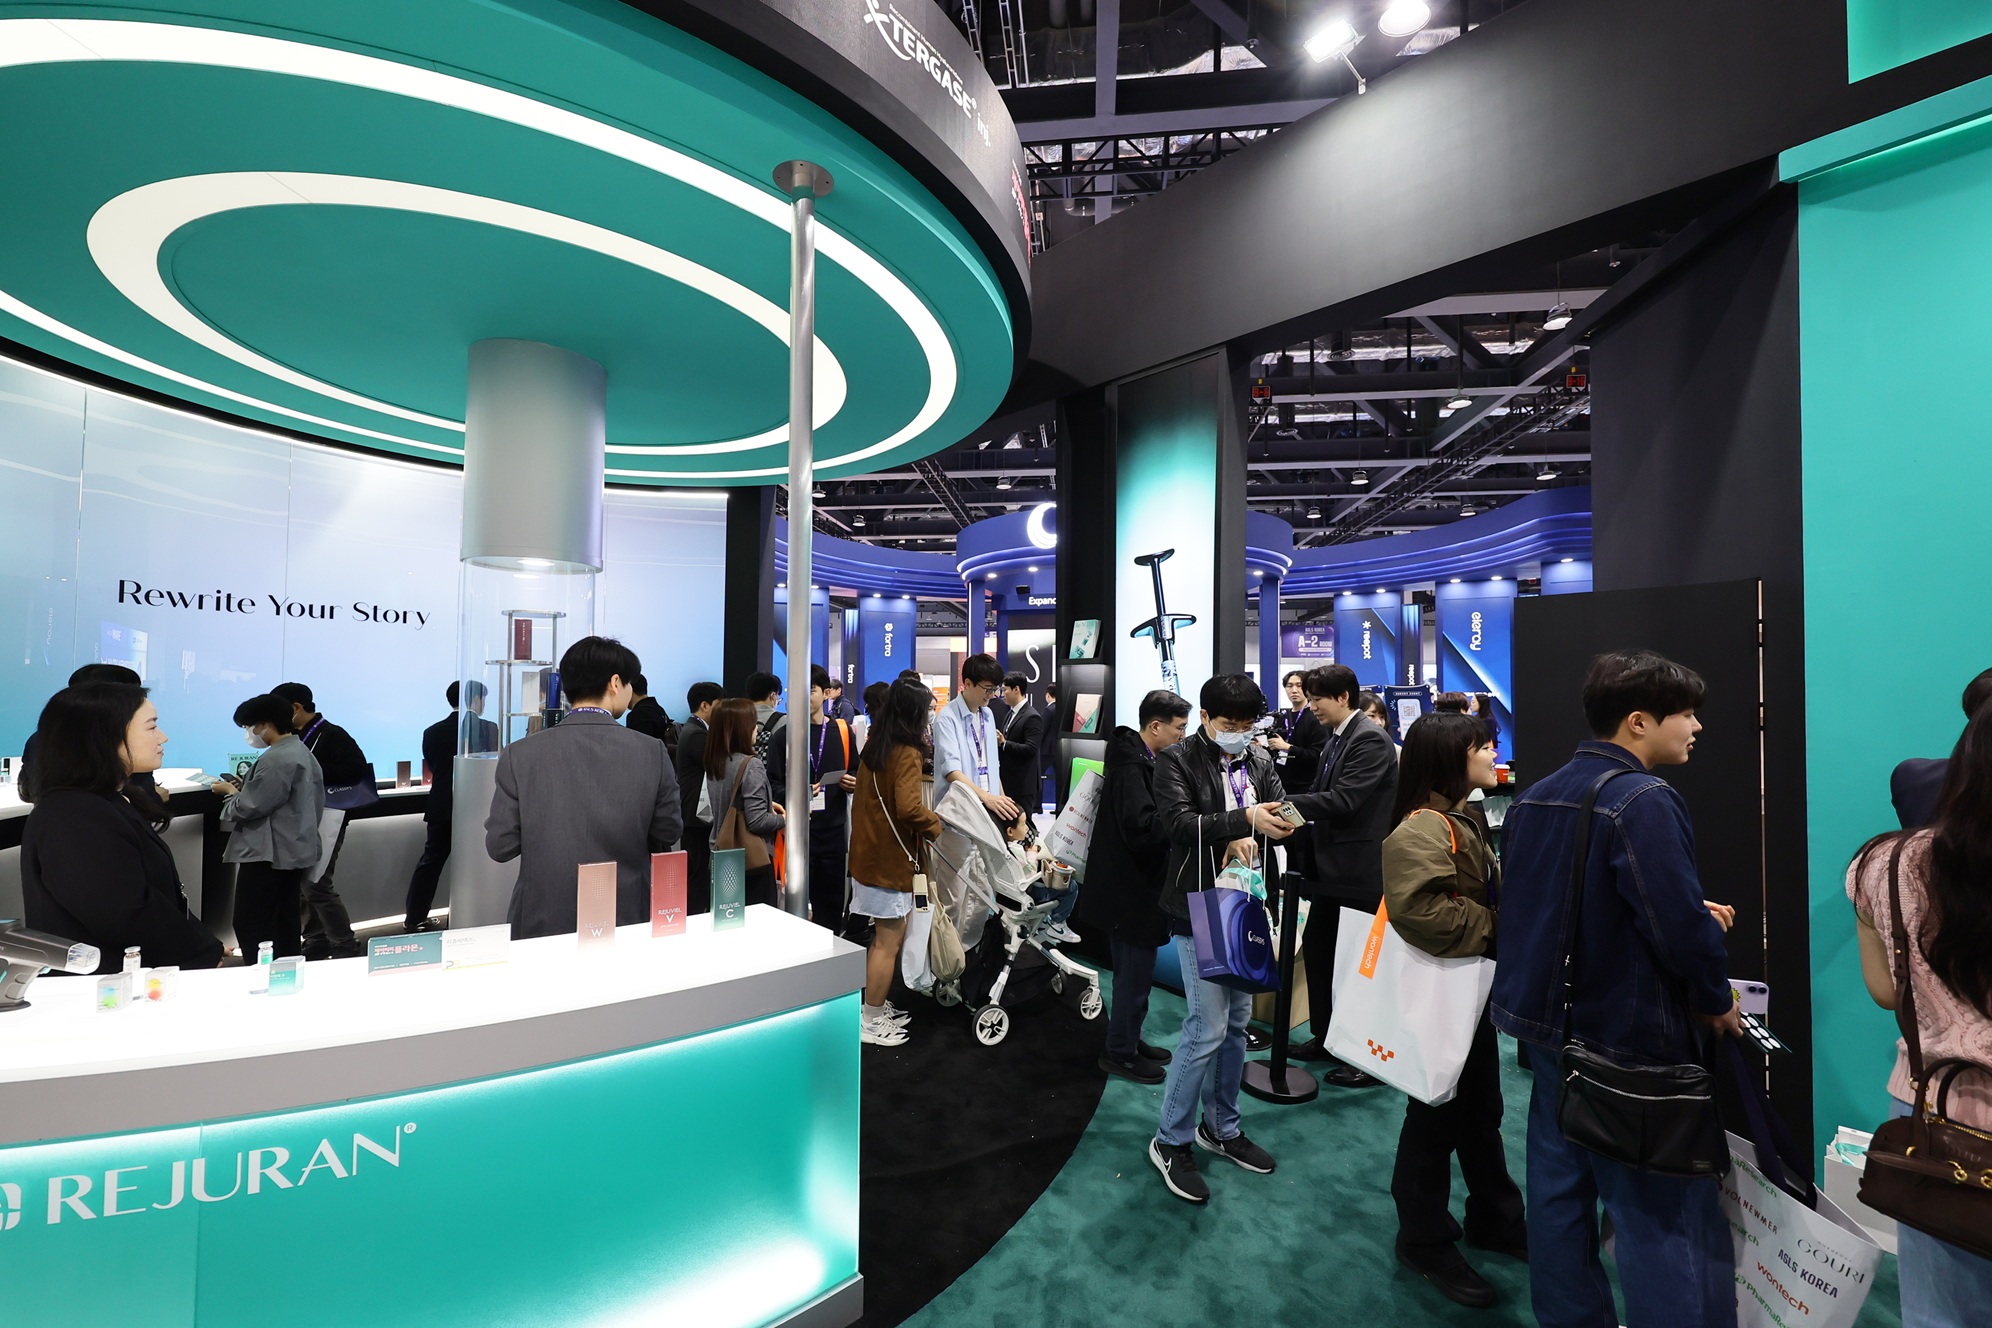
SEOUL, South Korea | Oct 23 — More than 5,000 healthcare professionals, researchers and industry stakeholders are expected to gather at ASLS Korea 2026 Autumn on Nov. 7-8, 2026, at COEX in Seoul, where 170 companies and more than 350 exhibition booths will showcase emerging technologies, clinical developments and innovations shaping the future of aesthetic medicine.

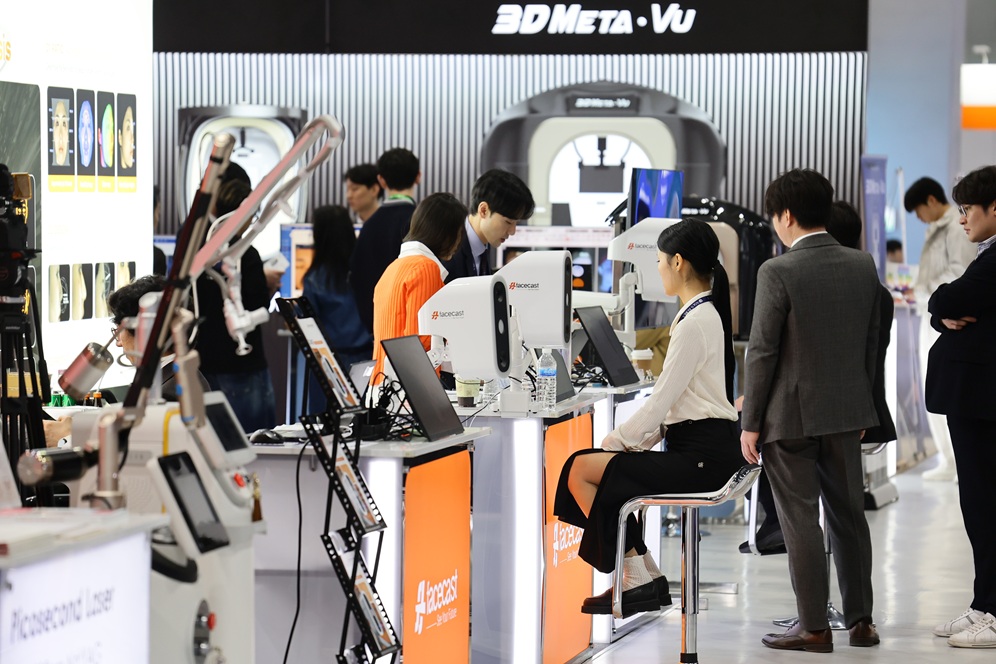
Attendees explore the latest medical aesthetic technologies and device innovations during an exhibition at ASLS Korea, where manufacturers showcase advancements in laser systems, energy-based devices, injectables and regenerative medicine.

The event will highlight the latest developments in aesthetic medicine, with manufacturers and solution providers presenting new technologies across laser systems, energy-based devices, injectables and regenerative medicine. Exhibitors are expected to showcase innovations aimed at improving treatment precision, patient outcomes and clinical workflows, reflecting key trends driving growth in the global medical aesthetics sector.

Latest Medical Aesthetic Technologies and Regenerative Treatments to Be Showcased at ASLS Korea 2026 Autumn


New-Generation Laser Platforms and Energy-Based Devices Highlight Industry Trends

A major focus of this year’s exhibition will be the evolution of laser technology. Manufacturers are expected to present new-generation laser platforms designed to deliver greater precision, customization and treatment versatility across a broad range of dermatological and aesthetic indications. These systems continue to evolve beyond traditional applications, integrating advanced energy-delivery mechanisms and user-friendly interfaces to support increasingly personalized treatment approaches.

Energy-based devices will also feature prominently at the exhibition. Technologies utilizing radiofrequency, ultrasound and other energy modalities are gaining attention for their ability to address skin tightening, body contouring and rejuvenation with minimal downtime. The latest systems entering the market are designed to offer improved treatment consistency while helping practitioners respond to growing patient demand for nonsurgical aesthetic procedures.

The industry’s continued shift toward regenerative aesthetics is expected to be reflected in a broad range of injectable and regenerative solutions showcased during the event. From advanced injectable products to therapies focused on stimulating the body’s natural repair processes, exhibitors will present innovations aimed at supporting long-term aesthetic outcomes and expanding treatment options available to practitioners.

Latest Medical Aesthetic Technologies and Regenerative Treatments to Be Showcased at ASLS Korea 2026 Autumn

Device Innovation, AI and Regenerative Aesthetics Drive Industry Transformation

Artificial intelligence (AI) and digital technologies are becoming increasingly integrated into aesthetic medicine, and ASLS Korea 2026 Autumn will demonstrate how these tools are influencing modern clinical practice. The exhibition is also expected to serve as a platform for new products entering the aesthetic medicine market.

Participating companies are expected to introduce newly developed devices and technology solutions while offering visitors opportunities to experience their capabilities through live demonstrations and hands-on presentations. Such demonstrations can provide clinicians with insights into practical applications, treatment protocols and real-world performance.

The convergence of device innovation, regenerative science and AI reflects a broader transformation taking place across the industry. Through its combination of exhibitions, scientific exchange and clinical learning opportunities, the event will bring together stakeholders from across the global aesthetics community to explore emerging trends and technologies shaping the future of aesthetic medicine.

Healthcare professionals interested in attending ASLS Korea 2026 Autumn can find additional information on registration, the exhibition and the scientific program at https://www.asls.kr.


ICBA, OpenAI Announce Strategic Alliance to Bring Frontier AI Cybersecurity Capabilities to Community Banks

Washington, D.C. | Oct 23 — The Independent Community Bankers of America (ICBA) and OpenAI today announced a landmark strategic alliance to help community banks access AI-enabled cybersecurity capabilities, training, and peer-to-peer engagement. The alliance builds on ICBA’s broader advocacy to ensure community banks are included as advanced AI capabilities are developed and deployed.

Earlier this year, ICBA led development of the Secure & AI-Ready America Action Plan, which called for federal action to address AI-enabled cybersecurity risks and expand access to advanced defensive capabilities for critical infrastructure providers. The partnership connects that priority with OpenAI’s Daybreak for Frontline Defenders, creating a pathway for community banks to access advanced cyber capabilities, training, and technical support.

“Community banks do not need to navigate the AI era alone,” ICBA President and CEO Rebeca Romero Rainey said. “Through our new alliance, ICBA and OpenAI are helping ensure community bankers have a seat at the table as some of the world’s most advanced cybersecurity capabilities are developed and deployed. Our members will have opportunities to learn directly from leading AI experts, explore defensive capabilities, and share lessons learned so they can make informed decisions that strengthen the resilience of their institutions and the communities they serve.”

“Protecting America’s financial infrastructure means making sure community banks have access to advanced tools to defend it,” said OpenAI Head of National Security Policy Sasha Baker. “Through Daybreak for Frontline Defenders and our work with ICBA, we’re helping put AI-powered cyber defenses within reach of the banks that Main Street depends on—with the training and support to use them effectively. The strength of a bank’s defenses shouldn’t depend on the size of its technology budget.”

What this Alliance Means for Community Banks

Through this alliance, eligible ICBA member banks will have a pathway to explore OpenAI’s Daybreak for Frontline Defenders, which is designed to support defensive cybersecurity work, including vulnerability identification and validation, threat investigation, authorized security testing, remediation support, risk prioritization, and other cybersecurity workflows.

The alliance will also provide ICBA-member community banks with:

Subsidized access to Daybreak for Frontline Defenders for eligible institutions in accordance with OpenAI’s program requirements.

ICBA member-exclusive education and training with OpenAI experts.

ICBA’s new AI Show-n-Tell sessions, providing a practical forum for community banks to demonstrate real-world AI use cases, discuss implementation challenges, and share lessons learned.

The AI Adoption group on ICBA Community, ICBA’s peer-to-peer network of more than 8,000 community bankers allowing members to exchange resources, questions, and practical experiences.

Together, ICBA and OpenAI aim to make advanced cybersecurity capabilities more practical and accessible for community banks, whether an institution is ready to explore frontier AI today or is still developing its AI strategy. As these technologies evolve, ICBA and OpenAI will continue working to identify sustainable, cost-effective approaches that enable community banks of varying sizes and technical maturity to participate and benefit.